SAML authentication for Status Pages.
Restrict access to internal or sensitive status updates.
Rootly now supports SAML authentication for Status Pages, enabling you to restrict access to internal or sensitive status information using your organization’s identity provider. This gives enterprise teams a secure, centralized way to share incident updates and service health—without exposing details publicly or managing separate credentials.
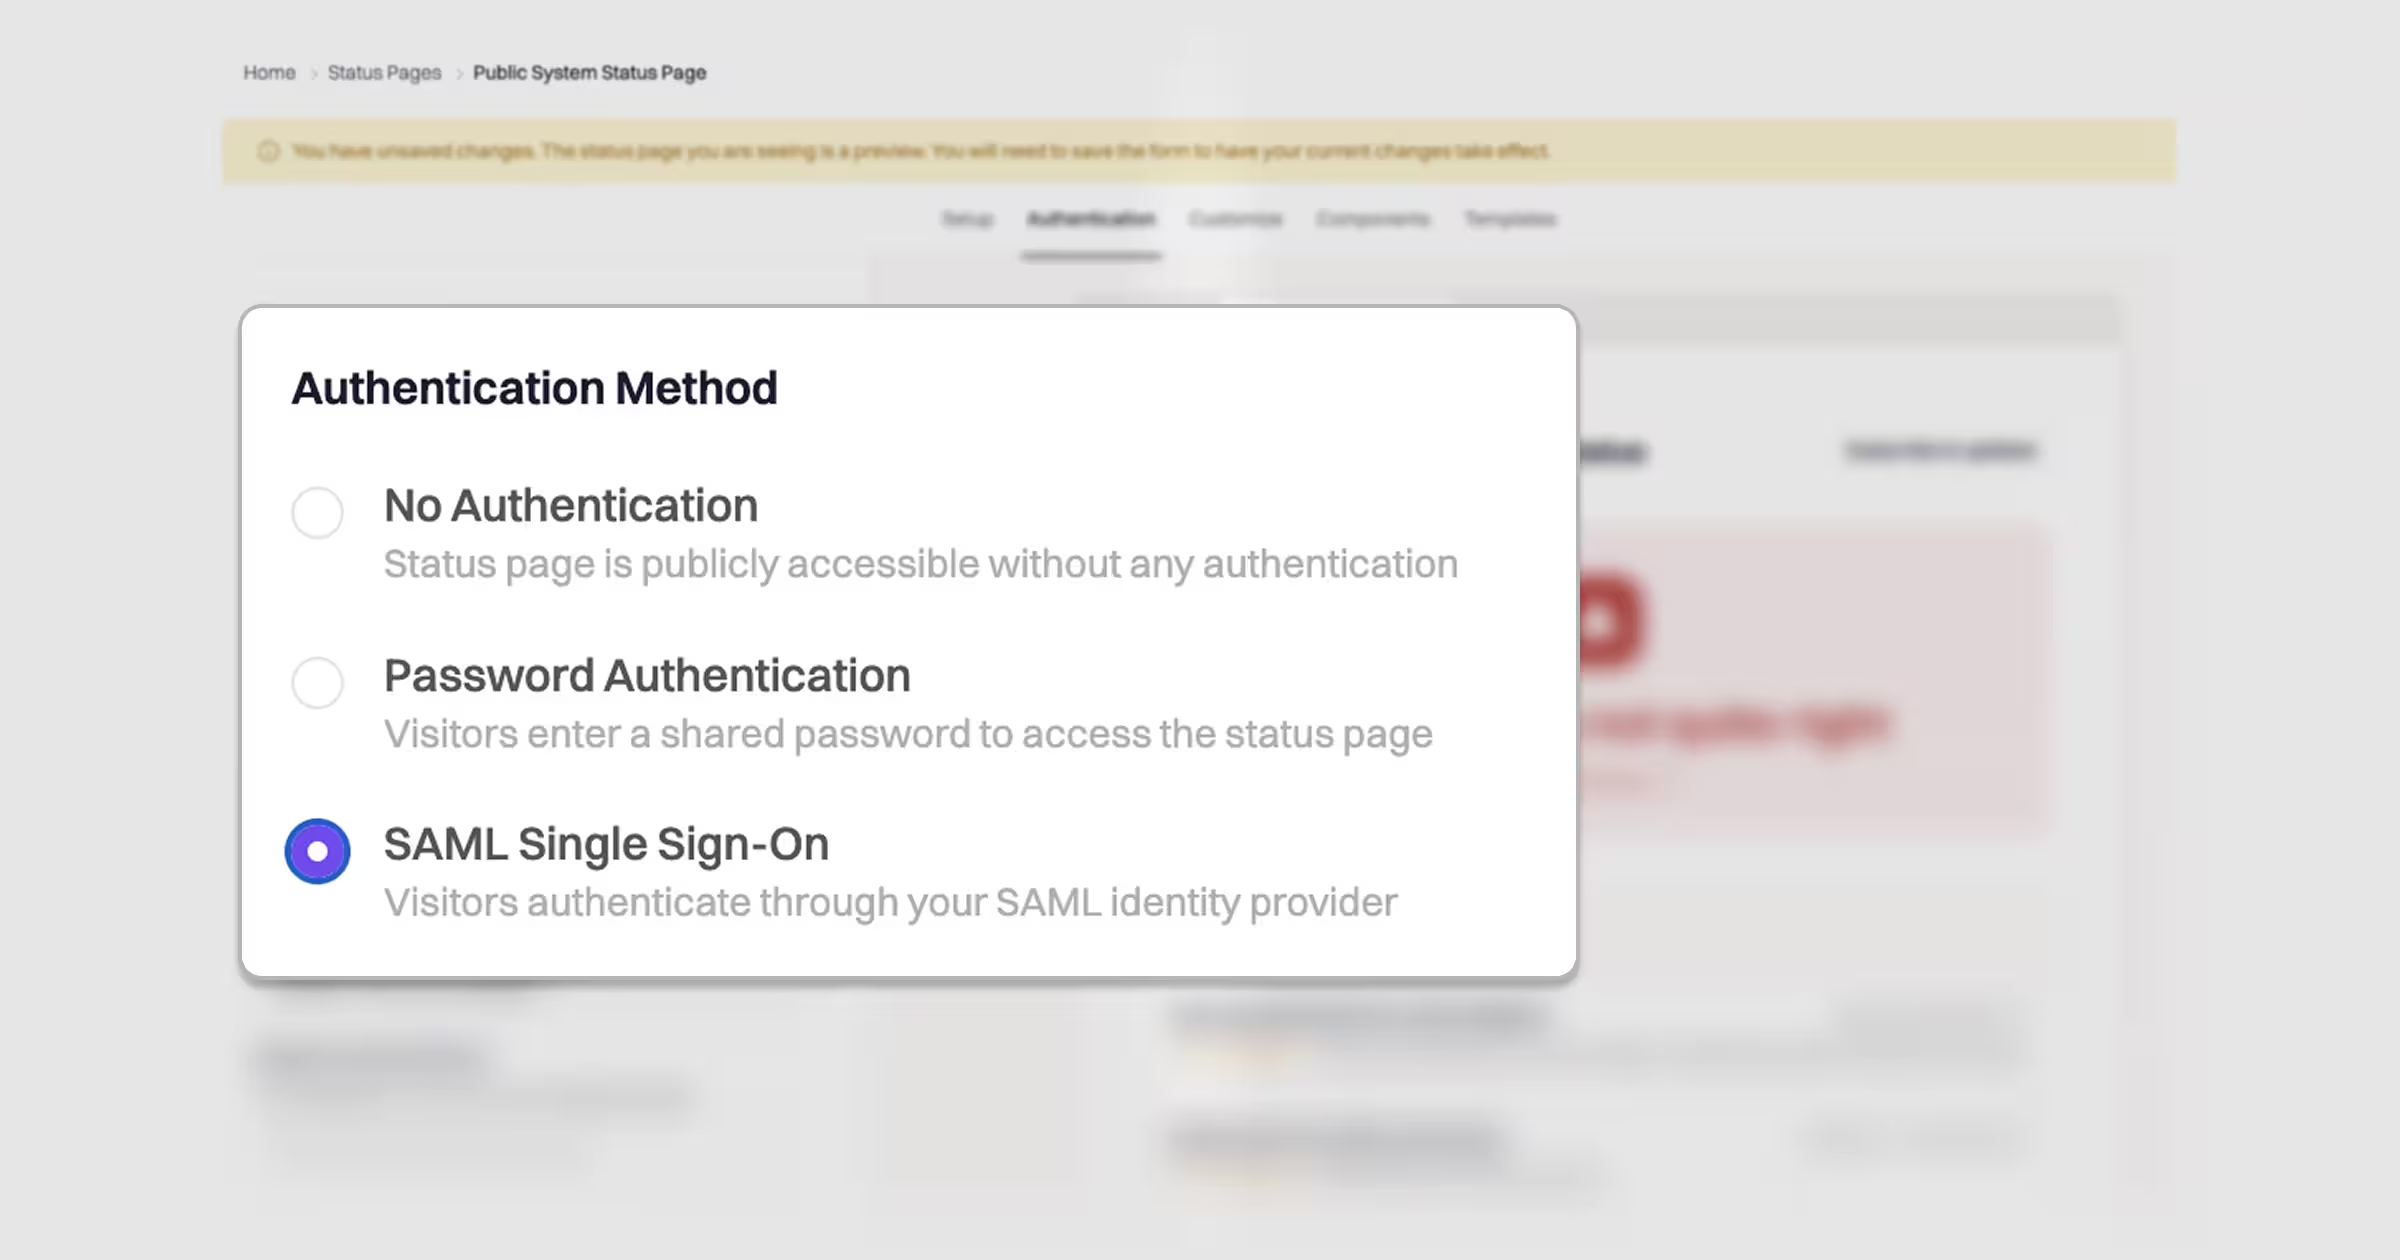
Rootly’s SAML configuration UI for Status Pages.
Why it matters
Status Pages aren’t always meant for the public internet. Many organizations use them to communicate internally, with customers, or with partners during sensitive incidents. With SAML authentication, you can now:
- Enforce single sign-on (SSO): Require users to authenticate via your existing IdP (Okta, Azure AD, etc.) before viewing a Status Page.
- Reduce access risk: Eliminate the need for shared passwords or manually managed access lists.
- Meet enterprise security standards: Align Status Pages with your organization’s broader identity and access management policies.
Check out the documentation to learn more and get SAML configured for your status pages.
Related changelogs
From sign up to incident-ready in minutes.
One command sets up your team, on-call, alerting, and status page, then pages your phone to prove it works.
Live mode on the Alerts view.
A new Live Mode toggle on the Alerts view streams incoming alerts in real time.
The Rootly Edge Connector
Connect your internal systems to Rootly without exposing them to the public internet.